Quantum architecture detection and response

Securing the quantum computing stack.

Quantum Offense is developing a new generation of security solutions to protect enterprise investments in quantum software. From low-level qubit instructions to the development environments where quantum software is built.

Founded in Spring 2025. Operating in stealth while researching exploits for quantum computing platforms and the forensic and detection methodologies needed to secure them.

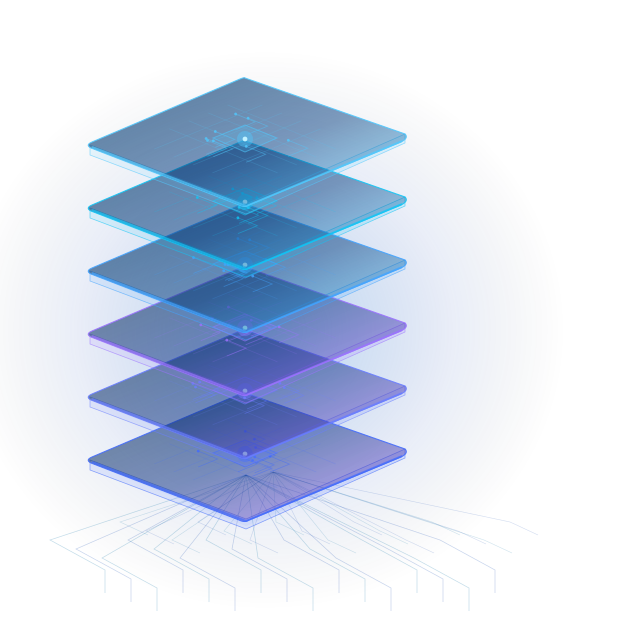
Six connected planes representing the quantum computing research stack.
  1. Human & development environments
  2. Applications & libraries
  3. Runtime & toolchains
  4. Compilers & transpilers
  5. Qubit instructions
  6. Quantum hardware
Research & Development Focus

About Quantum Offense

Researching threats to quantum computing.

Founded in Spring 2025, Quantum Offense is conducting private research into threats to quantum computing platforms and the forensic methods needed to investigate, detect, and protect against them.

Our work spans the quantum computing stack, from low-level instructions to human-driven development environments. We are translating that research into a new generation of detection and response solutions for enterprises investing in quantum software, backed by some of the most experienced engineers in the fields of threat detection and prevention.

Quantum Offense is seed-backed and advised by accomplished leaders in cybersecurity.

Founder

Gary Golomb

Chief Research Officer

Gary Golomb has spent 25 years building companies and developing solutions to complex problems in threat research, digital forensics, machine learning, and detection engineering.

He cofounded Awake Security, one of the first Network Detection and Response (NDR) platforms. Awake was named a "Best Places to Work" in Silicon Valley, and was recognized as the #1 most advanced NDR in the NAV Forrester Wave after being acquired by Arista Networks. He was the first employee and researcher at Cylance, the company credited with developing the first fully AI-based EDR that operated at scale, making traditional antivirus obsolete. He joined NetWitness early after it acquired Proventsure, an endpoint data discovery and forensics product company he cofounded. His work in exploit analysis and intrusion detection dates to the Dragon IDS in 2001.

His current work focuses on threats to quantum computing platforms and the forensic capabilities needed to understand them.